Monday, October 12, 2026
Mostly Cloudy, 78°Wind: mph,

Welcome to our new web site!
To give our readers a chance to experience all that our new website has to offer, we have made all content freely avaiable, through October 1, 2018.
During this time, print and digital subscribers will not need to log in to view our stories or e-editions.

Data security is critical in today’s digital world, especially for law firms that handle sensitive client information. A lack of cybersecurity efforts can lead to data breaches, resulting in financial losses, reputational damage and even safety risks for you and your clients. However, as lawyers, your expertise lies in the law, not IT systems.
Managed IT services can bridge the knowledge and skill gap by offering advanced technologies, 24/7 monitoring services, compliance solutions and support. Frontline Managed Services explains the details in this article.
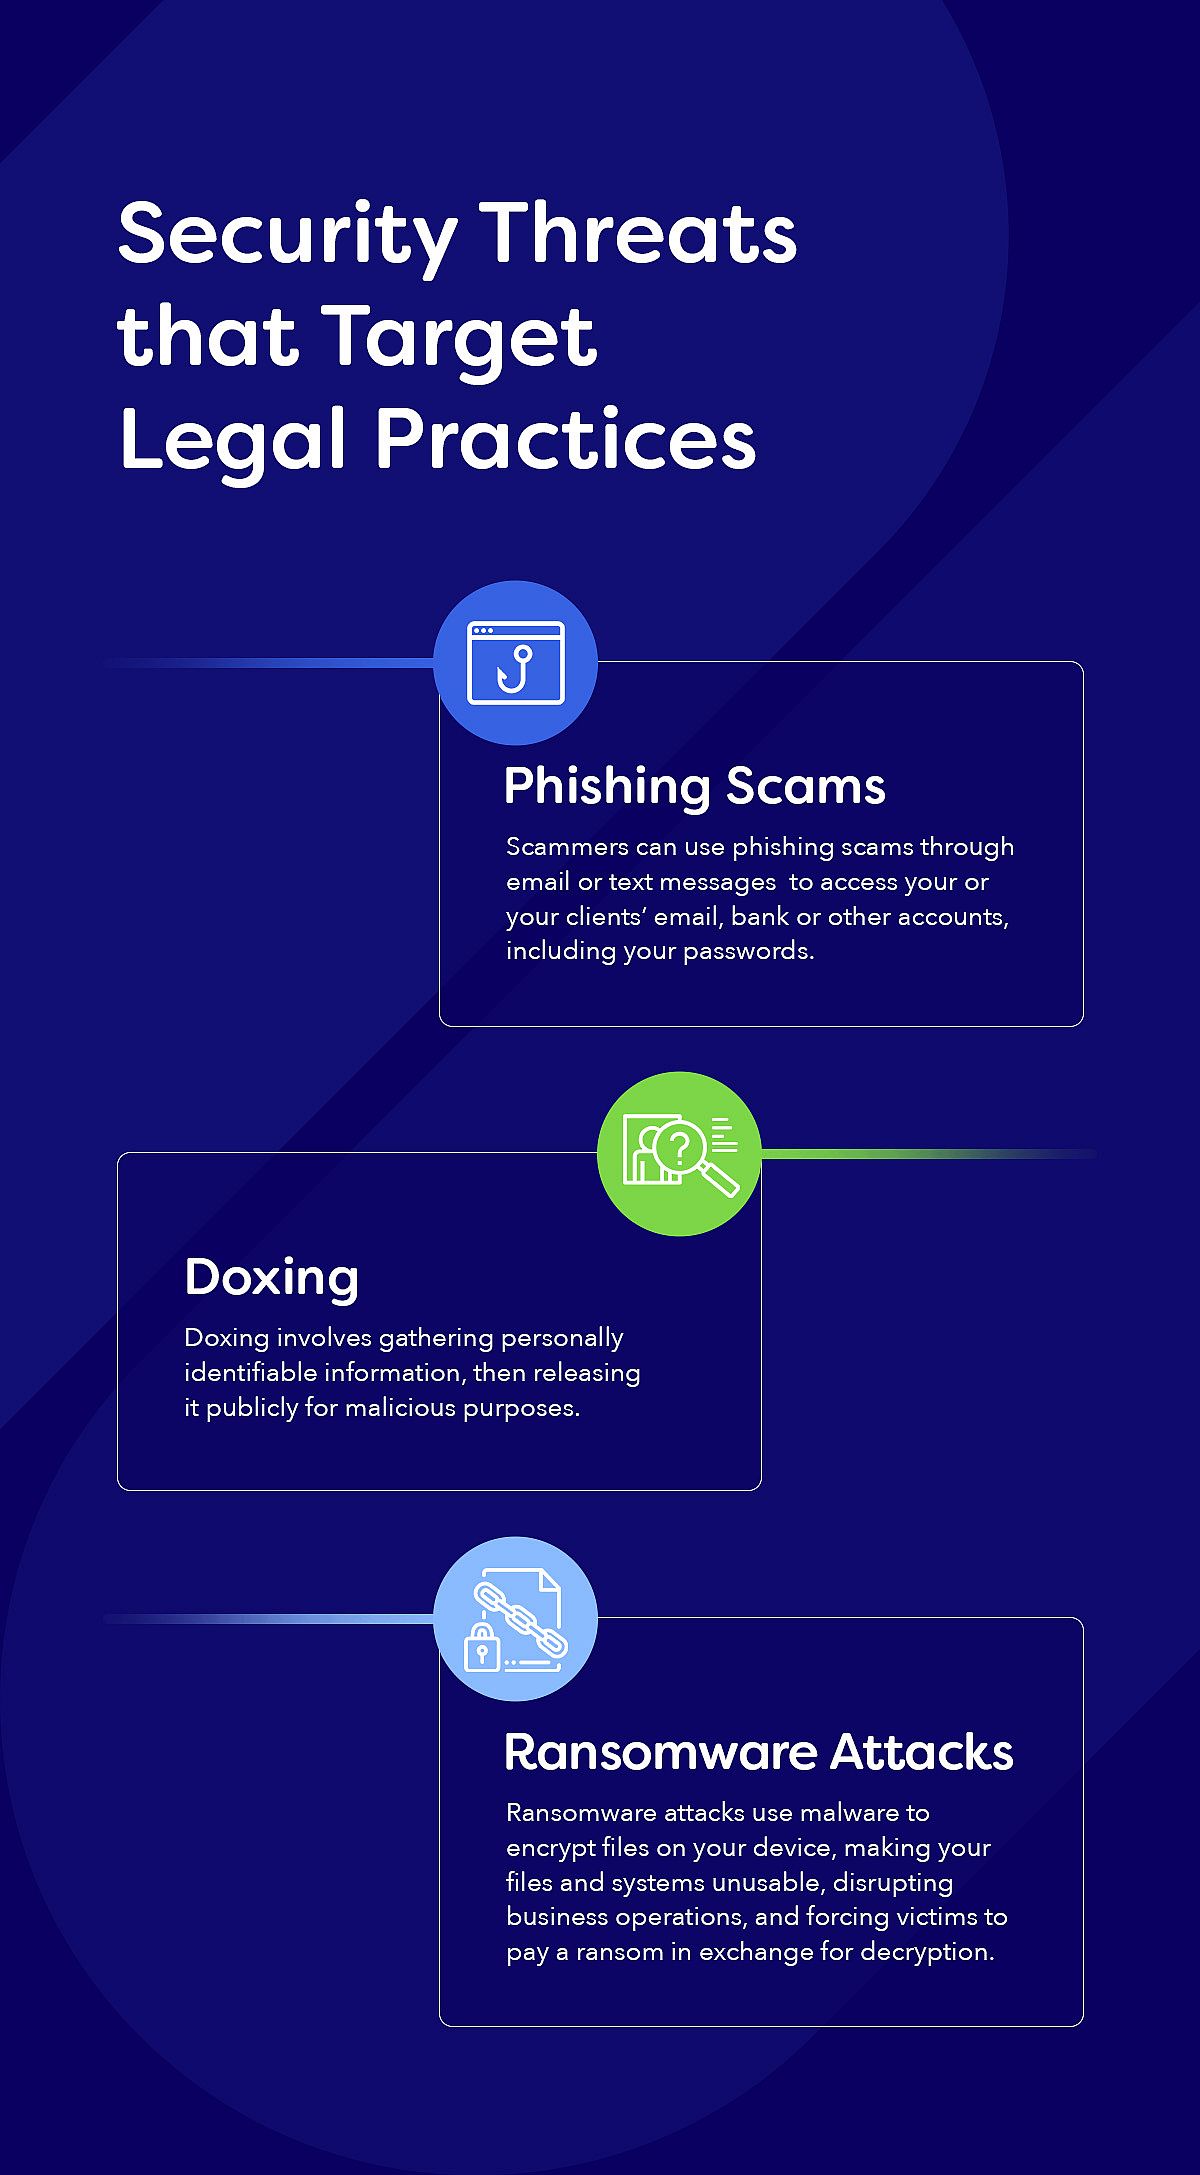
Your law firm is susceptible to social engineering attacks as long as you work with sensitive and valuable information. Social engineering attacks involve psychologically manipulating people into providing confidential information by performing specific actions. Scammers may aim to disrupt your operations, gain unauthorized access or commit fraud. With technological advancements, the techniques involved in these threats are also evolving.
In 2024, 42% of organizations reported experiencing social engineering attacks. Some attacks you need to be mindful of include:
Apart from digital attacks, you should also be wary of physical ones. For instance, a scammer may impersonate an IT support representative in person, before inserting a device into your computer to steal sensitive information. They then use this information to extort you or your clients.
Managing cyber threats and preventing data breaches is part of your professional responsibility as lawyers. You handle sensitive information daily, whether through document collaboration, e-signing contracts, legal research or workflow automation. These activities make you an attractive target for hackers. Taking safety precautions is especially essential for a remote and hybrid workforce.
The American Bar Association (ABA)’s Model Rules of Professional Conduct indicate you should take reasonable steps to protect client information. Specific model rules that apply to cybersecurity include:
States may also have their own professional conduct rules, often based on these model rules. As law professionals, you must stay on top of these data protection requirements. If you’re an international law firm, you must also understand privacy laws in other countries.
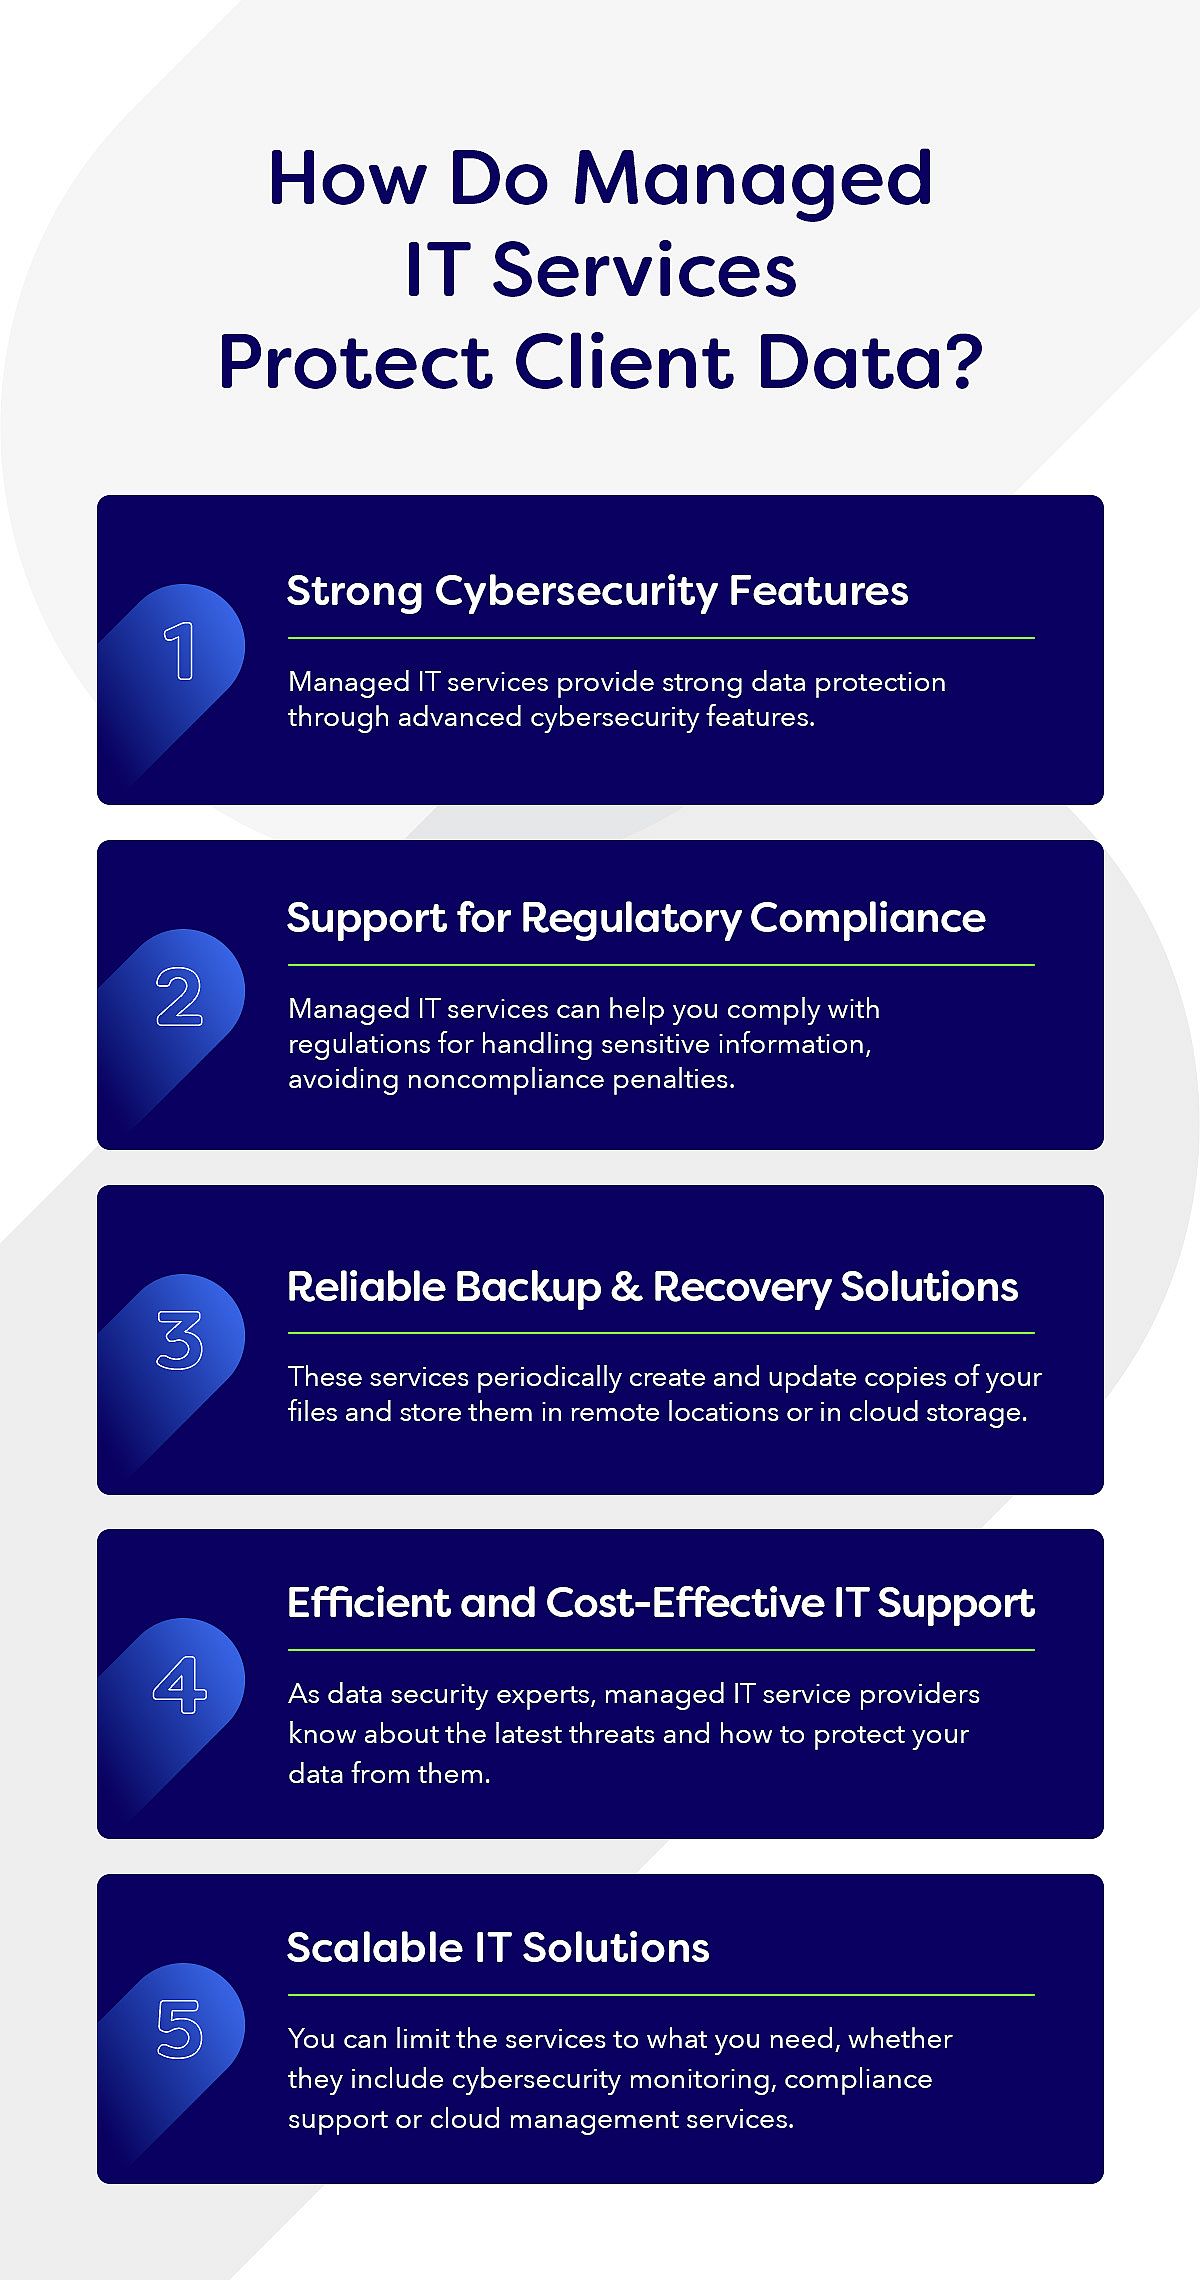
Managed IT services can help protect your client data through the services they offer, which can include:
1. Strong Cybersecurity Features
Managed IT services provide strong data protection through advanced cybersecurity features. They offer security assessments to identify your vulnerabilities and highlight areas for improvement. They also monitor your systems 24/7, detecting and responding to issues immediately before the damage escalates. Since scammers don’t function on a regular schedule, continuous monitoring is essential.
Managed IT teams use technology that detects patterns of potential attacks from real-time data. Once they identify unusual activity in your system, automated alerts can inform responsible teams of potential breaches. Analytics also examines past incidents to foresee future vulnerabilities. IT teams can then refine security protocols as needed.
2. Support for Regulatory Compliance
Managed IT services can help you comply with regulations for handling sensitive information, thus avoiding noncompliance penalties. They also provide recovery solutions in the event of a data breach. For instance, you may be handling medical records due to personal injury or medical malpractice cases. In this case, you must comply with the Health Insurance Portability and Accountability Act (HIPAA).
HIPAA requires you to protect people’s identifiable health information, whether electronically, orally or on paper, which includes:
If your law firm engages in financial activities, such as financial advisory, tax preparation or real estate services, the FTC Safeguards Rule also requires you to keep customer information secure. After a data breach, the FTC suggests that you:
HIPAA’s Breach Notification Rule requires you to notify affected individuals within 60 days. A resolution agreement may also apply, where you must perform specific obligations and report to the Department of Health and Human Services (HHS) for about three years. The HHS will monitor your compliance within this period. Managed IT services can help you comply with the reporting requirements.
3. Reliable Backup and Recovery Solutions
Adhering to regulations involves adopting recovery solutions. However, recovery solutions are only effective with sufficient backups. Managed IT services regularly back up your files and systems to ensure business continuity and minimize downtime. These services periodically create and update copies of your files and store them in remote locations or in cloud storage.
IT services encrypt and regularly test these backups, ensuring they’re free from data corruption. With backups in place, recovery solutions can use the copies to reestablish access to your files, applications, data or other resources. Without these systems, retrieving lost data can take hours or days, impeding business operations. These consequences can be severe, especially if they involve lost, altered or compromised evidence in legal cases.
4. Efficient and Cost-Effective IT Support
Managed IT service providers know about the latest threats and how to protect your data from them. Engaging managed IT services can be more cost-effective than building an in-house team. You’ll also avoid the costs of investing in your own equipment.
Some managed IT services leverage automation and artificial intelligence (AI). For instance, a provider may use an AI-powered service desk to make workflow efficient and reduce resolution periods. They can also provide support for your in-house teams, if you have any. They can offer employee training and share best practices in handling cybersecurity risks.
The cost of lost time and resources due to potential data breaches can be substantial. Long-term costs also include reputational damage and strained attorney-client relationships. With this in mind, investing in a managed IT service provider can be worth it. They can fill the skill gap in your company without increasing your capital expenses.
5. Scalable IT Solutions
Small to medium-sized law firms can especially benefit from outsourcing IT management. You can limit the services to what you need, whether they include cybersecurity monitoring, compliance support or cloud management services. Growing and established firms also benefit from tailored services, no matter the complexity of their infrastructure. Managed IT services have the capacity to scale:
Some managed IT services are better than others. You might even encounter malicious actors posing as IT experts. To ensure you’re selecting a trusted and reliable provider, look for:
As law professionals, it’s your responsibility to ensure your clients’ information is well-protected. Managed IT services can play a significant role, as they can help you navigate the increasing cyber risks that come with advancing technology. These services can also protect you and your company, ensuring malicious actors can’t steal your information and identity. Given the consequences of data breaches, investing in managed IT services can be worth the cost.
Depending on the provider, covered services can include:
Consider working with those who have extensive industry expertise. Certifications and a proven track record also show if you’re looking at a trusted company. Tailored professional services ensure you’re getting the solutions you need.
This story was produced by Frontline Managed Services and reviewed and distributed by Stacker.


