Thursday, October 1, 2026
Clear, 65°Wind: mph,

Welcome to our new web site!
To give our readers a chance to experience all that our new website has to offer, we have made all content freely avaiable, through October 1, 2018.
During this time, print and digital subscribers will not need to log in to view our stories or e-editions.

Without a cybersecurity plan, your business is more vulnerable to cyberattacks, data breaches, financial losses, operational downtime and reputational damage. When an incident happens, the lack of a clear plan can leave teams scrambling to identify the problem, protect affected systems and keep the business moving while costs and risks continue to grow.
Over the last year, 56% of U.S. small businesses experienced at least one cyberattack. When these attacks lead to data breaches, ransomware, downtime or exposed customer information, the costs can continue long after systems are restored.
Businesses need to understand the cybersecurity risks they face, how these threats can impact their operations and what they can do to reduce their exposure. Here, iuvo breaks down the risks every business should know and why a cybersecurity plan is a foundational strategy.
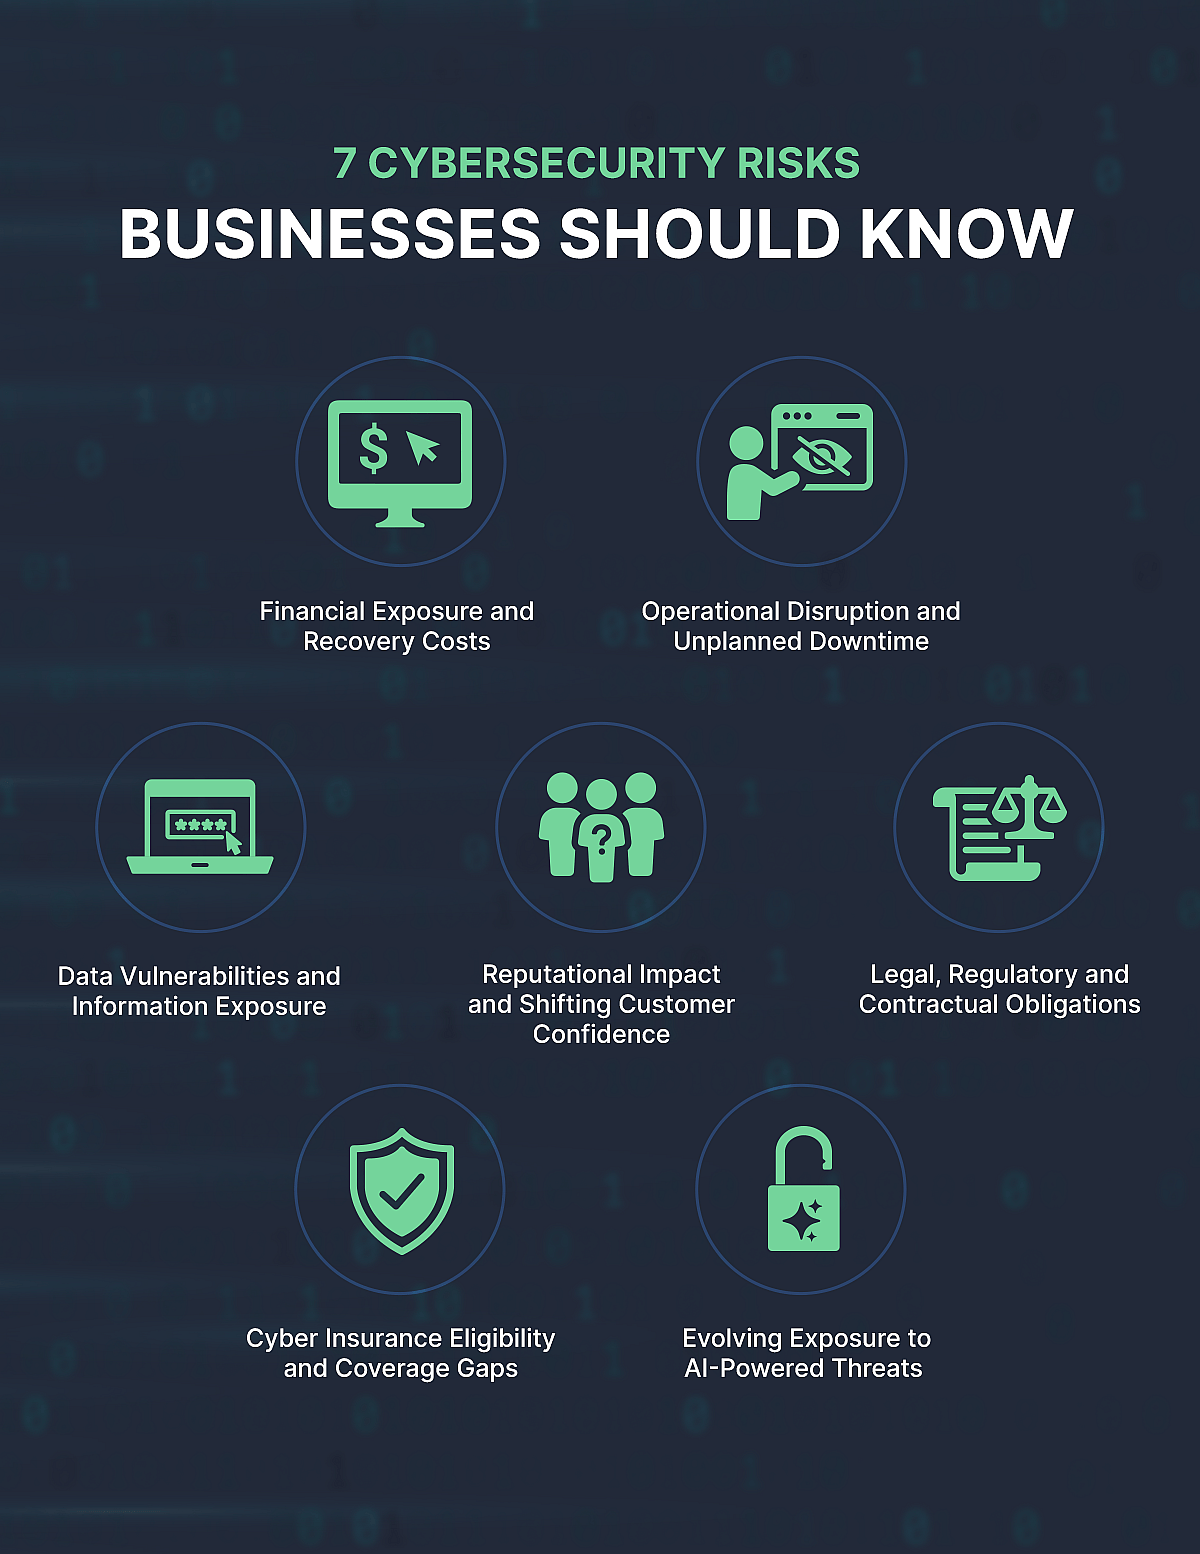
A cyberattack can create costs that continue to affect businesses long after the initial incident. To find the source of the attack and restore operations, businesses may need to pay for investigations, legal support, system restoration and customer notifications while also losing revenue during downtime.
Recent breach and ransomware data show how quickly these costs can add up:
Cyberattacks can quickly turn from a security issue into a business continuity issue. When systems go down or data becomes inaccessible, teams may be unable to serve customers, complete internal work or maintain normal operations. Without a coordinated response plan, downtime can last longer, recovery can move more slowly and productivity losses can grow.
In 2025, organizations took an average of 241 days to identify and contain a cyber breach, resulting in nearly eight months of exposure and response activity, per the IBM report. Ransomware recovery timelines vary, but only 53% of ransomware-affected organizations fully recovered within a week, per the Sophos report.
The impact can also reach the people responsible for response and recovery. In the Sophos report, every organization that had data encrypted in a ransomware attack reported direct repercussions for its IT and cybersecurity team, including increased stress, guilt and, in 25% of cases, leadership replacement. The human cost of operating without an incident response plan compounds the technical, operational and financial challenges.
Sensitive data is one of the most valuable assets a business holds, and a common target for cybercriminals. Customer records, financial information, employee data and intellectual property all need clear protections. Without a cybersecurity plan, businesses may not have a reliable way to identify where sensitive data lives, who can access it or how it should be protected.
The risks increase when that data is exposed. In 2025, customer personally identifiable information (PII) was the most stolen or compromised data type, per the IBM report, appearing in 53% of breaches. Employee PII was stolen or compromised in 37% of incidents, while intellectual property appeared in 33%.
Data risk also extends beyond internal systems. Information held by vendors, partners or service providers may also be vulnerable. A comprehensive data protection strategy should account for both internal and external data flows so critical assets are not left exposed.
A cyber incident can affect how customers, partners and investors view a business long after systems are restored. If sensitive data is exposed or operations are disrupted, customers may question whether the organization can protect their information and provide reliable service. For businesses in data-sensitive industries like financial services, biotech or professional services, that loss of confidence can be especially difficult to repair.
The market impact can also be measurable. In a 2025 AON analysis, major cyber incidents resulted in an average 9% decrease in shareholder value in the year following the event. Of 1,407 cyber events analyzed, 49 developed into reputation risk events, resulting in a 27% decline in shareholder value.
Certain attack types may create greater reputational risk than others. In the 2025 Hiscox Cyber Readiness Report, malware and ransomware attacks accounted for approximately 60% of reputation risk cyber events, and 29% of SMBs that experienced a cyberattack reported negative publicity as a direct consequence.
Without a cybersecurity plan, businesses may face legal, regulatory and contractual issues at the same time. These risks can be especially serious for organizations in heavily regulated industries like financial services, biotech and life sciences, where data protection is tied directly to compliance and business continuity.
Key areas of exposure include:
The financial impact also varies by industry. Healthcare breaches cost an average of $7.42 million per incident, according to IBM, while financial services breaches averaged $5.56 million per incident. For businesses in these sectors, cybersecurity compliance regulations are part of protecting operations, customers and long-term stability.
Cyber insurance can help businesses recover after an incident, but it does not replace a strong cybersecurity plan. Insurers often want to see that basic protections are already in place before approving or renewing coverage. If those controls are missing or undocumented, a business may have fewer policy options or face complications when filing a claim.
These insurance-related risks are becoming more common:
AI is changing how cybercriminals plan and carry out attacks. With AI, attackers can create more convincing phishing messages, test new tactics faster, scale campaigns across more targets, and uncover security gaps that may have gone undetected. A cybersecurity plan can help businesses keep pace with these AI-driven risks by updating employee training, response procedures and security tools, including AI-enabled defenses where appropriate.
A cybersecurity plan helps businesses keep pace with those changes. It gives teams a way to update employee training, security policies and response procedures as AI-driven risks evolve. Understanding how AI affects your IT environment can also help your business make smarter decisions about access controls, data protection and long-term security planning.
A strong cybersecurity plan starts with a clear view of how attackers gain access to business systems, data and networks. Today, businesses face several common threats.
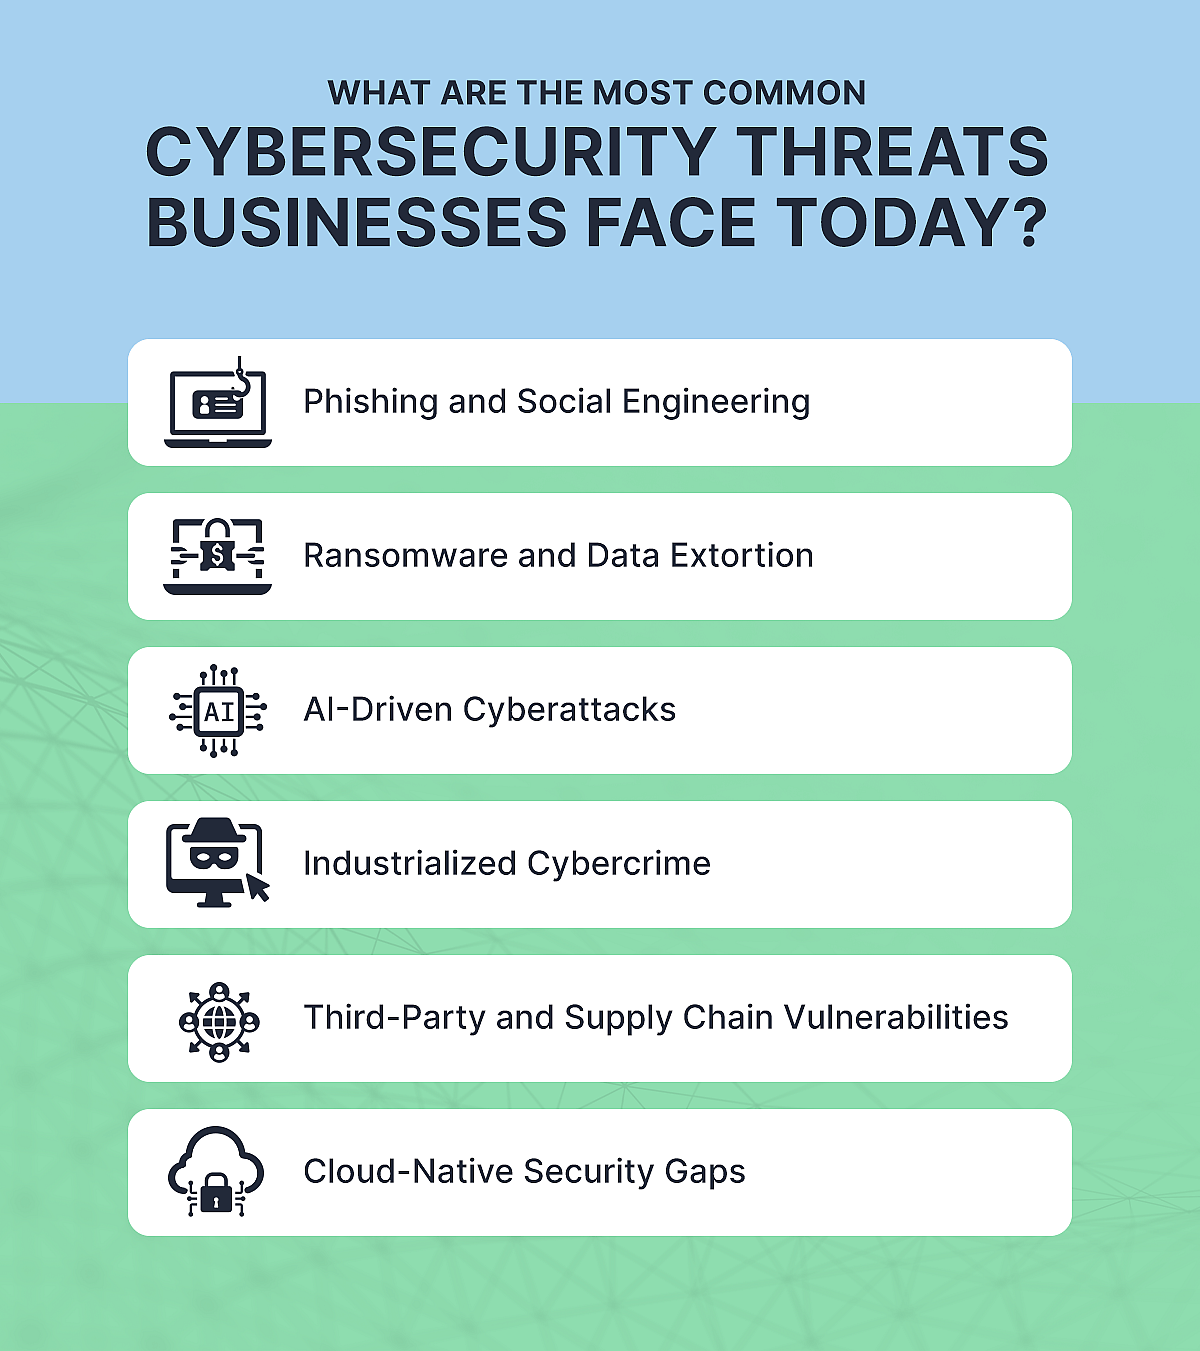
Attackers use phishing to send an email, text or message that can trick an employee into sharing credentials, downloading malware or sending money to the wrong account. As AI tools become more common, these messages can also sound more personal and convincing, making them harder to spot.
In 2025, phishing accounted for 16% of all breaches studied, per IBM, with human involvement as a factor in approximately 60% of cases. AI-generated phishing emails have become more convincing, which makes the risk more difficult to manage. Targets are 4.5 times more likely to click AI-generated phishing emails than traditionally crafted messages, per the Center for Strategic and International Studies (CSIS).
Reducing phishing risk takes both technology and training. Security awareness programs help employees recognize suspicious messages, report potential threats and avoid actions that can give attackers access to larger systems. Without that support, phishing can become the entry point for a much larger incident.
Ransomware can stop normal operations by locking teams out of critical systems or data. In many cases, attackers can also steal information and threaten to release it publicly if the business does not pay. This situation creates both an operational crisis and a data exposure risk.
Smaller organizations may have fewer resources to prevent and recover from these attacks. However, paying a ransom does not guarantee a full recovery. Effective incident response planning can reduce the likelihood of a successful ransomware attack and help businesses recover faster if one occurs.
AI is giving attackers new ways to make existing cyberthreats more convincing and harder to detect. It can help them write stronger phishing messages, test variations faster, develop more evasive malware and automate attacks across a wider set of targets.
Recent data shows how quickly this risk is growing. AI-enabled cyberattack activity grew by 89% from 2024 to 2025, according to the CSIS, and some organizations are already seeing breaches tied to AI models or applications. These trends make AI governance an important part of cybersecurity planning.
Many organizations are still catching up. Nearly two-thirds lack AI governance policies, per IBM, which can leave gaps around access, acceptable use, data protection and response planning.
Cybercrime has become more organized and easier to scale. Rather than relying solely on one-off attacks, many cybercriminals now use automated tools and repeatable tactics to find vulnerable businesses faster.
This shift challenges the idea that cybercriminals only target one type of organization. Different types of businesses can be attractive targets for different reasons:
Attackers can use automated tools to scan thousands of potential targets at once, so risk is not limited to a single industry or company size. An unpatched system, weak access controls or exposed data can be enough to put a business in their path.
A business's cybersecurity also depends on the vendors, partners and software providers it works with. Even if internal systems are well protected, a third party with weak security practices can create an opening for attackers. This risk is especially important for regulated businesses that share sensitive data with outside organizations. These incidents can also take longer to resolve because the affected systems, data and responsibilities may span multiple organizations.
A strong cybersecurity plan should include vendor qualification and ongoing management to ensure external partners meet security expectations and do not weaken the business's overall security.
Cloud adoption can help businesses move faster, but it can also make security harder to manage. Data may live across public cloud, private cloud and on-premises systems, while employees may also use outside AI tools as part of their daily work.
Without clear oversight, it becomes harder to know where sensitive information is stored, who can access it and which settings may create risk. That visibility gap can slow response after a cyberattack. In 2025, per IBM’s 2026 report, 30% of breaches involved data distributed across multiple environments.
Clear policies for cloud services, AI platforms and access controls help reduce those risks before they turn into data exposure.
A cyber incident can continue to affect a business long after systems are restored. Revenue, customer relationships, market position and day-to-day operations may all feel the impact for months or even years.
Long-term consequences can include:
For businesses in regulated industries such as financial services, biotech and life sciences, the long-term effects can also include ongoing regulatory scrutiny and sustained customer skepticism. Building cyber resilience before an incident occurs can be far less costly than rebuilding trust, operations and momentum afterward.
A cybersecurity plan is strongest when it connects security decisions to business priorities. Strategic IT planning helps leaders identify which systems, data and workflows carry the most risk, then prioritize the investments that will make the biggest difference.
A strong cybersecurity plan gives businesses a practical way to reduce risk, respond faster and make better security decisions over time. Instead of treating cybersecurity as a one-time project, the plan should guide ongoing work across people, systems, vendors and compliance needs.
Key components include:
This story was produced by iuvo and reviewed and distributed by Stacker.


